APIlize
Every application eventually needs more than one client - web, mobile, desktop, or something you haven't built yet. An API-first architecture is what lets you add the next one without touching the last one.
The alternative is worse than it sounds. Giving a mobile app direct database credentials means shipping login access inside the app itself. Scope it down to a limited-access account instead, and you're now managing per-client permissions by hand - a problem that only gets harder as access levels change over time. Most of what goes wrong here is human error, not malicious intent.
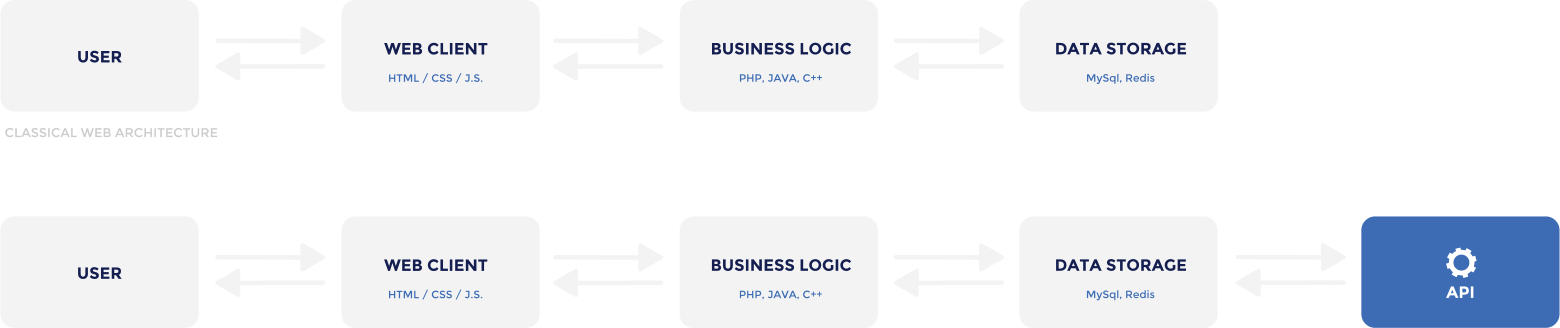
An API layer removes the tradeoff. Change the logic behind it without shipping a client update. Get the security right once, at the boundary, instead of re-litigating it every time you add a client.
If APIlizing your application means adding new clients to the roadmap, we can help plan them and build them.